

Pass Microsoft AZ-800 exam questions - convert Test Engine to PDF
Pass Your AZ-800 Exam Easily - Real AZ-800 Practice Dump Updated Sep 22, 2026
NEW QUESTION # 143
You have a server that runs Windows Server and contains a shared folder named UserData.
You need to limit the amount of storage space that each user can consume in UserData.
What should you use?
- A. Storage Spaces
- B. Distributed File System (DFS) Namespaces
- C. File Server Resource Manager (FSRM)
- D. Work Folders
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/storage/fsrm/fsrm-overview
NEW QUESTION # 144
Your network contains an Active Directory domain, a web app named App1, and a perimeter network. The perimeter network contains a server named Server1 that runs Windows Server.
You plan to provide external access to App1.
You need to implement the Web Application Proxy role service on Server1.
Which role should you add to Server1, and which role should you add to the network? To answer, drag the appropriate roles to the correct targets. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
Answer:
Explanation:
NEW QUESTION # 145
You have an Azure virtual machine named VM1 that runs Windows Server.
You perform the following actions on VM1:
Create a folder named Folder1 on volume C.
Create a folder named Folder2 on volume D.
Add a new data disk to VM1 and create a new volume that is assigned drive letter E.
Install an app named App1 on volume E.
You plan to resize VM1.
Which objects will present after you resize VM1?
- A. Folder1, Folder2, App1, and volume E
- B. Folder1 and Folder2 only
- C. Folder1, volume E, and App1 only
- D. Folder1 only
Answer: C
Explanation:
The folder 2 is on D: which by default is the scratch disk that is wiped on a re-boot, a re-size of the VM requires a reboot of the VM, therefore the contents of D will be wiped.
NEW QUESTION # 146
Case Study 3 - ADatum Corporation
Overview
Company Information
ADatum Corporation is a manufacturing company that has a main office in Seattle and two branch offices in Los Angeles and Montreal.
Fabrikam Partnership
ADatum recently partnered with 2 company named Fabrikam, Inc.
Fabrikam is a manufacturing company that has a main office in Boston and a branch office in Orlando.
Both companies intend to collaborate on several joint projects.
Existing Environment
ADatum AD DS Environment
The on-premises network of ADatum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The forest contains two domains named adatum.com and east.adatum.com and the domain controllers shown in the following table.
Fabrikam AD DS Environment
The on-premises network of Fabrikam contains an AD DS forest named fabrikam.com.
The forest contains two domains named fabrikam.com and south.fabrikam.com.
The fabrikam.com domain contains an organizational unit (OU) named Marketing.
Server Infrastructure
The adatum.com domain contains the servers shown in the following table.
HyperV1 contains the virtual machines shown in the following table.
All the virtual machines on HyperV1 have only the default management tools installed.
SSPace1 contains the Storage Spaces virtual disks shown in the following table.
Azure Resources
ADatum has an Azure subscription that contains an Azure AD tenant. Azure AD Connect is configured to sync the adatum.com forest with Azure AD.
The subscription contains the virtual networks shown in the following table.
The subscription contains the Azure Private DNS zones shown in the following table.
The subscription contains the virtual machines shown in the following table.
All the servers are in a workgroup.
The subscription contains a storage account named storage1 that has a file share named share1.
Requirements
Planned Changes
ADatum plans to implement the following changes:
- Sync Data1 to share1.
- Configure an Azure runbook named Task1.
- Enable Azure AD users to sign in to Server1.
- Create an Azure DNS Private Resolver that has the following configurations:
- Name: Private1
- Region: West US
- Virtual network: VNet1
- Inbound endpoint: SubnetB
- Enable users in the adatum.com domain to access the resources in the south.fabrikam.com domain.
Technical Requirements
ADatum identifies the following technical requirements:
- The data on SSPace1 must be available always.
- DC2 must become the schema master if DC1 fails.
- VM3 must be configured to enable per-folder quotas.
- Trusts must allow access to only the required resources.
- The users in the Marketing OU must have access to storage1.
- Azure Automanage must be used on all supported Azure virtual machines.
- A direct SSH session must be used to manage all the supported virtual machines on HyperV1.
Drag and Drop Question
You need to implement the planned change for Data1.
Which actions should you perform in sequence? To answer, drag the appropriate actions to the correct order. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.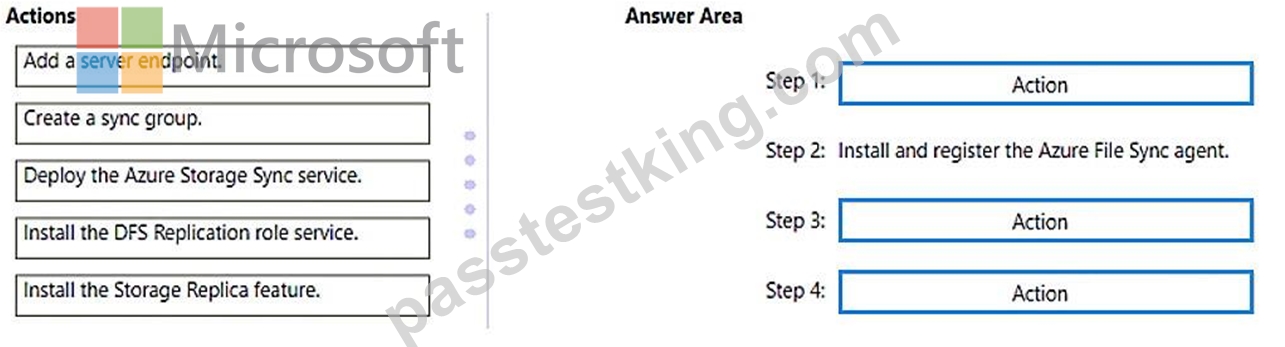
Answer:
Explanation:
NEW QUESTION # 147
SIMULATION
Task 8
You need to deploy a new primary DNS zone named fabrikam.com to DC1. The zone must be signed.
Answer:
Explanation:
See the solution of this Task below
Explanation:
To deploy a new primary DNS zone named fabrikam.com to DC1 and sign the zone, you can follow these steps:
Step 1: Create the Primary DNS Zone Use the Add-DnsServerPrimaryZone PowerShell command to create the primary zone:
Add-DnsServerPrimaryZone -Name "fabrikam.com" -ZoneFile "fabrikam.com.dns" -DynamicUpdate Secure This command creates a primary zone for fabrikam.com with a DNS file named fabrikam.com.dns and allows secure dynamic updates.
Step 2: Sign the Zone To sign the zone, you can use the DNS Manager or Windows PowerShell. Here's how to sign the zone using PowerShell:
Add-DnsServerSigningKey -ZoneName "fabrikam.com" -Type KeySigningKey -CryptoAlgorithm RsaSha256 Set-DnsServerDnsSecZoneSetting -ZoneName "fabrikam.com" -DenialOfExistence NSEC3 -NSEC3Parameters 1,0,10,"" These commands add a signing key to the zone and set DNSSEC settings with NSEC3 parameters.
Step 3: Publish the Signed Zone After signing the zone, ensure that it is published and available for DNS queries. You can verify the zone signing status using the following command:
Get-DnsServerZone -Name "fabrikam.com"
Note: Ensure that you have the appropriate permissions to perform these actions on DC1 and that the DNS Server role is installed and properly configured. Also, replace "fabrikam.com.dns" with the actual path to your DNS file if it's different12.
By following these steps, you should be able to deploy and sign the new primary DNS zone fabrikam.com on DC1.
NEW QUESTION # 148
Hotspot Question
You need to sync files from an on premises server named Server1 to Azure by using Azure File Sync.
You have a cloud tiering policy that is configured for 30 percent free space and 70 days.
Volume E on Server1 is 500 GB.
A year ago, you configured E:\Data on Server1 to sync by using Azure File Sync. The files that are visible in E:\Data are shown in the following table.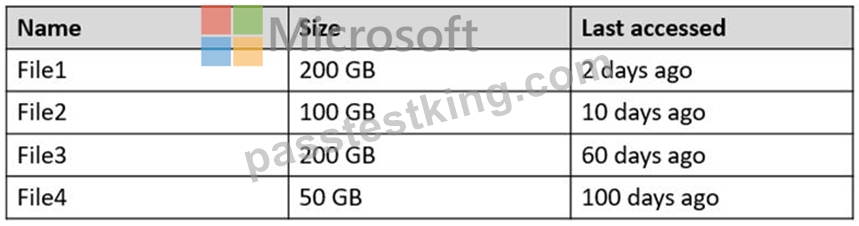
Volume E does NOT contain any other files.
Where are File1 and File3 located? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
The volume free space policy will always take precedence; when there isn't enough free space on the volume to store as many days worth of files as described by the date policy, Azure File Sync will override the date policy and continue tiering the coldest files until the volume free space percentage is met.
https://docs.microsoft.com/en-us/azure/storage/file-sync/file-sync-cloud-tiering-policy
NEW QUESTION # 149
You need to meet the technical requirements for VM3
On which volumes can you enable Data Deduplication?
- A. C and D only
- B. D and E only
- C. C, D, E, and F
- D. D only
- E. D, E, and F only
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/storage/data-deduplication/interop
Topic 2, Fabrikam inc.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements, if the case study has an All Information tab. note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
Fabrikam, Inc. Is a manufacturing company that has a main office In New York and a branch office in Seattle.
On-premises Servers
The on-premises network contains servers that run Windows Server as shown in the following table.
DC1 hosts all the operation master roles.
WEB1 and WEB2 run an Internet Information Services (IIS) web app named Webapp1.
On-premises Network
The New York and Seattle offices are connected by using redundant WAN links.
The client computers in each office get IP addresses from their local DHCP server.
DHCP! contains a scope named Scope1 that has addresses for the New York office. DHCP2 contains a scope named Scope2 that has addresses for the Seattle office.
Group Policy Object (GPOs)
The cwp.fabrikam.com domain contains the organizational units (OUs) and custom Group Policy Objects (GPOs) shown in the following table.
Requirements:
Fabrikam Identifies the following planned changes:
* Create a single Azure subscription named Sub1 that will contain a single Azure virtual network named Vnet1.
* Replace the WAN links between the Seattle and New York offices by using Azure Virtual WAN and ExpressRoute. Both on-premises offices will be connected to Vnet1 by using ExpressRoute.
* Create three Azure file shares named newyorkfiles, seattfefiles, and companyfiles.
* Create a domain controller named dc3.corp.fabrikam,com in Vnet1.
* Deploy an Azure Virtual Desktop host pool lo Vnet1. The Azure Virtual Desktop session hosts will be hybrid Azure AD joined.
* License all servers for Microsoft Defender for servers.
* Use Azure Policy to enforce configuration management policies on the servers in Azure and on-premises.
Networking Requirements
Fabrikam identifies the following security requirements:
* Apply GP04 to the Azure Virtual Desktop session hosts. Ensure that Azure Virtual Desktop user sessions lock after being idle for 10 minutes. Users must be able to control the lockout lime manually from their client computer.
* Ensure that server administrators request approval before they can establish a Remote Desktop connection to an Azure virtual machine. If the request is approved, the connection must be established within two hours.
* Prevent user passwords from containing all or part of words that are based on the company name, such as Fab. fabrikam or fsbr! |.
* Ensure that all instances of Webapp1 use the same service account. The password of the service account must change automatically every 30 days.
* Prevent domain controllers from directly contacting hosts on the internet.
File Sharing Requirements
You need to configure the synchronization of Azure files to meet the following requirements:
* Ensure that seattlefiles syncs to FS2.
* Ensure that newyorkfiles syncs to FS1.
* Ensure that companyfiles syncs to both FS1 and FS2.
NEW QUESTION # 150
You have an Azure virtual machine named VM1 that runs Windows Server.
You need to configure the management of VM1 to meet the following requirements:
Require administrators to request access to VM1 before establishing a Remote Desktop connection.
Limit access to VM1 from specific source IP addresses.
Limit access to VM1 to a specific management port.
What should you configure?
- A. Azure Front Door
- B. Microsoft Defender for Cloud
- C. a network security group (NSG)
- D. Azure Active Directory (Azure AD) Privileged Identity Management (PIM)
Answer: B
Explanation:
https://docs.microsoft.com/en-us/azure/defender-fo
NEW QUESTION # 151
You have on-premises file servers that run Windows Server as shown in the following table.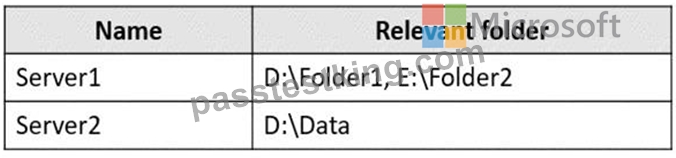
You have the Azure file shares shown in the following table.
You add a Storage Sync Service named Sync1 and an Azure File Sync sync group named Group1. Group1 uses share1 as a cloud endpoint.
You register Server1 and Server2 with Sync1. You add D:\Folder1 from Server1 as a server endpoint in Group1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, application, email Description automatically generated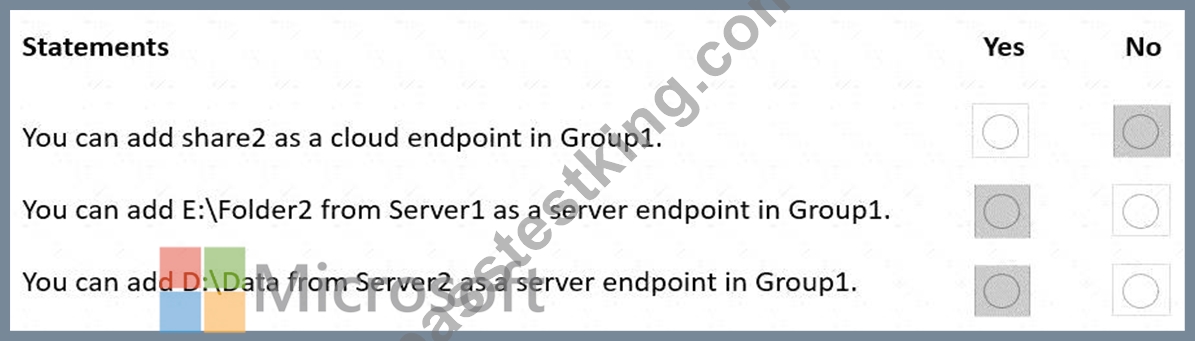
Reference:
https://docs.microsoft.com/en-us/azure/storage/file-sync/file-sync-planning
NEW QUESTION # 152
You have an Azure subscription that contains a virtual machine named VM1 as shown in the following exhibit.
The subscription has the disks shown in the following table.
Which disks can you attach as data disks to VM1?
- A. Disk1, Disk3, and Disk4 only
- B. Disk1, Disk2, Disk3. and Disk4
- C. Disk2 only
- D. Disk2 and Disk4 only
- E. Disk1 and Disk2 only
- F. Disk4 only
Answer: E
NEW QUESTION # 153
Your on-premises network contains an Active Directory domain named contoso.com. You have an Azure AD tenant. You plan to sync contoso.com with the Azure AD tenant by using Azure AD Connect cloud sync. You need to create an account that will be used by Azure AD Connect cloud sync. Which type of account should you create?
- A. user
- B. InetOrgPerson
- C. system-assigned managed identity
- D. group managed service account (gMSA)
Answer: D
Explanation:
In the AZ-800/"Administering Windows Server Hybrid Core Infrastructure" content, Azure AD Connect cloud sync uses a lightweight provisioning agent that reads from on-premises AD DS. The agent runs under a Group Managed Service Account (gMSA) so it can securely obtain and rotate credentials automatically. The implementation guidance states that during agent installation you provide domain admin credentials once so the installer can create and delegate a gMSA for the agent; alternatively, you can pre-create the gMSA and assign it. The documentation emphasizes that cloud sync does not rely on user or computer accounts with static passwords; instead it "deploys a gMSA for the agent service to ensure secure, automatic password management and least-privilege directory access." System-assigned managed identities apply to Azure resources only (not on-prem AD DS), and InetOrgPerson is an object class for users, not a service identity. A regular user account would introduce password management and rotation issues and is not the recommended nor required identity type for the cloud sync agent. Therefore, to satisfy Azure AD Connect cloud sync prerequisites, you create and use a gMSA.
NEW QUESTION # 154
You have a server named Server 1 that runs Windows Server and has the Hyper-V server role installed.
Server1 hosts a virtual machine named VM1. Server1 has an NV Me storage device that is assigned to VM1 by using Discrete Device Assignment.
You need to make the device available to the host.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation: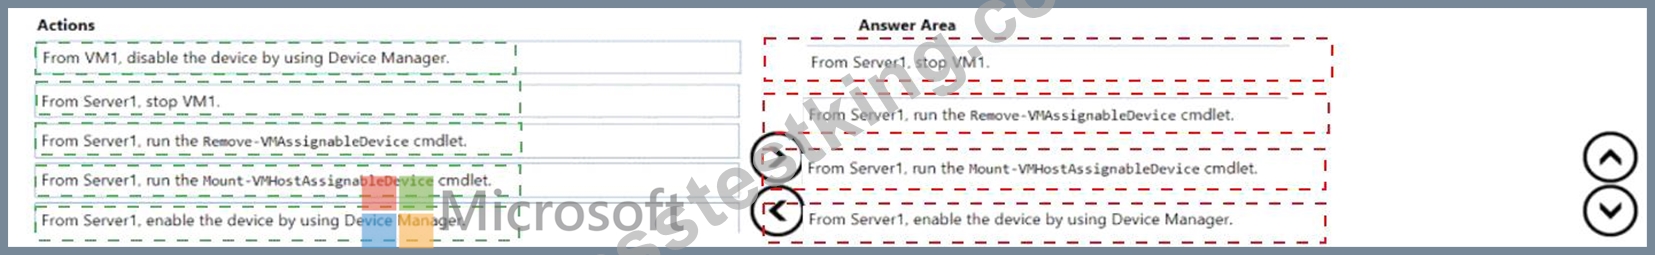
Explanation:
NEW QUESTION # 155
You have a server named Server1 that runs Windows Server Server1 has a just-a-bunch-of-disks (JBOD) enclosure attached.
You plan to create a storage pool on Server1 and a virtual disk that will use a mirror layout.
You are considering whether to use a two-way or a three-way mirror layout.
What is the minimum number of disks required for each type of minor layout? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 156
You need to meet the technical requirements for VM2.
What should you do?
- A. Implement shielded virtual machines.
- B. Implement Credential Guard.
- C. Enable enhanced session mode.
- D. Enable the Guest services integration service.
Answer: C
Explanation:
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more Information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements, if the case study has an All Information tab. note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
Fabrikam, Inc. Is a manufacturing company that has a main office In New York and a branch office in Seattle.
On-premises Servers
The on-premises network contains servers that run Windows Server as shown in the following table.
DC1 hosts all the operation master roles.
WEB1 and WEB2 run an Internet Information Services (IIS) web app named Webapp1.
NEW QUESTION # 157
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains the VPN servers shown in the following table.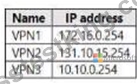
You have a server named NPS1 that has Network Policy Server (NPS) installed. NPS1 has the following RADIUS clients: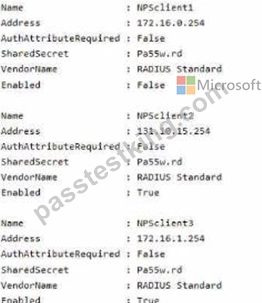
VPN1, VPN2, and VPN3 use NPS1 for RADIUS authentication. All the users in contoso.com are allowed to establish VPN connections. For each of the following statements, select Yes If the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Answer:
Explanation: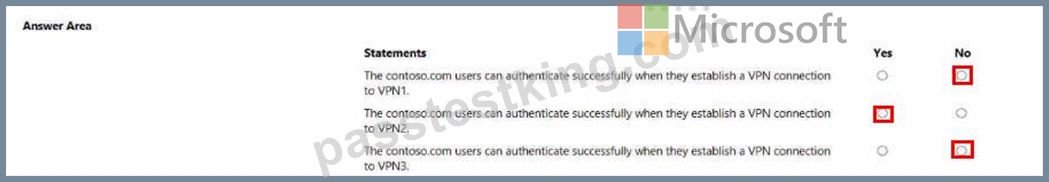
NEW QUESTION # 158
As an administrator, you're responsible for managing the security in hybrid as well as on- premises scenarios. While securing IPAM, which of the following would help you with defining the administrative domains of IPAM?
- A. None of the above
- B. IPAM Access Policies
- C. IPAM Access Scopes
- D. IPAM Roles
Answer: C
Explanation:
An access scope is responsible to decide which objects a user has access. Access scopes can be used for defining the IPAM administrative domains.
Reference:
https://docs.microsoft.com/en-us/learn/modules/implement-ip-address-management/4-administer- ip-address-management
NEW QUESTION # 159
Your company has offices in Boston and Montreal. The offices are connected by using a 10-Mbps WAN link that is often saturated The office in Boston contains the following:
* An Active Directory Domain Services (AD DS) domain controller named DC1.
* A server named Server1 that runs Windows Server and has the File Server role installed The office in Montreal contains 20 client computers that run Windows 10 Montreal does NOT have any servers.
The company plans to deploy a new line of business (LOB) application to all the client computers. The installation source files for the application are in \\Server\Apps.
Answer:
Explanation: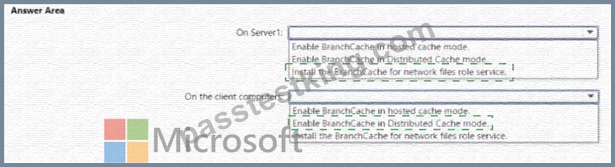
Explanation: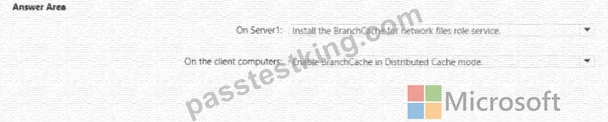
NEW QUESTION # 160
You need to meet the technical requirements for Server1. Which users can currently perform the required tasks?
- A. Admin3 only
- B. Admin1 and Admin3 only
- C. Admin1 only
- D. Admin1 Admin2. and Admm3
Answer: C
NEW QUESTION # 161
Which groups can you add to Group3 and Group5? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation: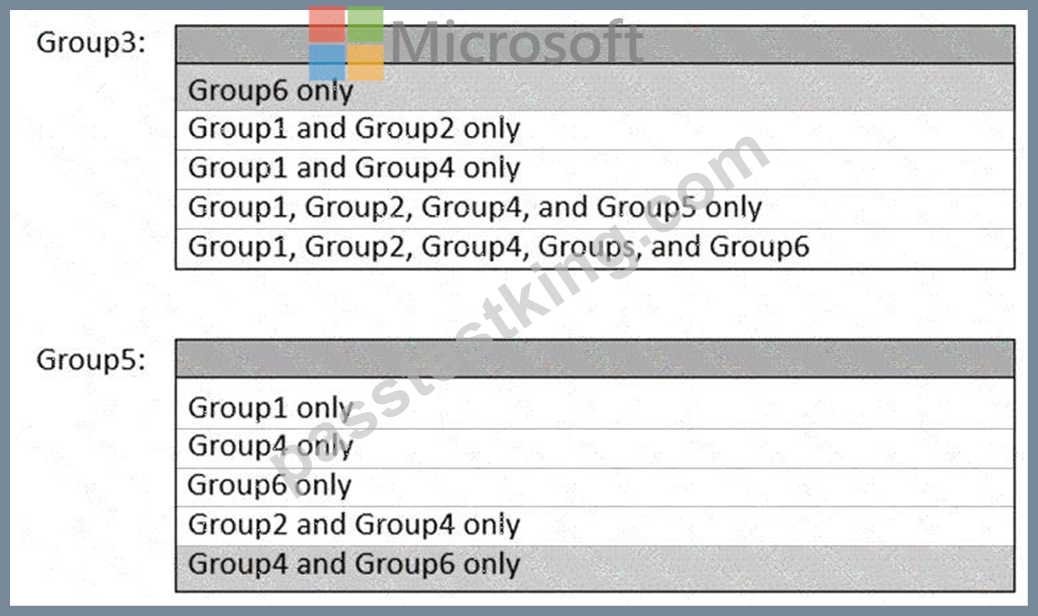
Reference:
https://docs.microsoft.com/en-us/windows/security/identity-protection/access-control/active-directory- security-groups
NEW QUESTION # 162
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three domains. Each domain contains 10 domain controllers.
You plan to store a DNS zone in a custom Active Directory partition.
You need to create the Active Directory partition for the zone. The partition must replicate to only four of the domain controllers.
What should you use?
- A. New-ADObjett
- B. Windows Admin Center
- C. dnscnd.exe
- D. DNS Manager
Answer: C
NEW QUESTION # 163
Hotspot Question
You plan to deploy an Azure virtual machine that will run Windows Server. The virtual machine will host an Active Directory Domain Services (AD DS) domain controller and a drive named F: on a new virtual disk.
You need to configure storage for the virtual machine. The solution must meet the following requirements:
- Maximize resiliency for AD DS.
- Prevent accidental data loss.
How should you configure the storage? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: F
Create a separate virtual data disk for storing the database, logs, and sysvol folder for Active Directory. Do not store these items on the same disk as the operating system.
Box 2: None
By default, data disks that are attached to a VM use write-through caching. However, this form of caching can conflict with the requirements of AD DS. For this reason, set the Host Cache Preference setting on the data disk to None.
Reference:
https://docs.microsoft.com/en-us/azure/architecture/reference-architectures/identity/adds-extend- domain
NEW QUESTION # 164
You have 10 on-premises servers that run Windows Server.
You plan to use Azure Network Adapter to connect the servers to the resources in Azure.
Which prerequisites do you require on-premises and in Azure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/manage/windows-admin-center/azure/use-azure-network-adapter
NEW QUESTION # 165
Which groups can you add to Group3 and Group5? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.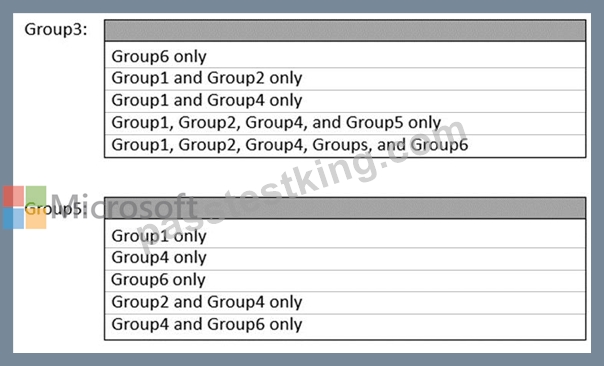
Answer:
Explanation: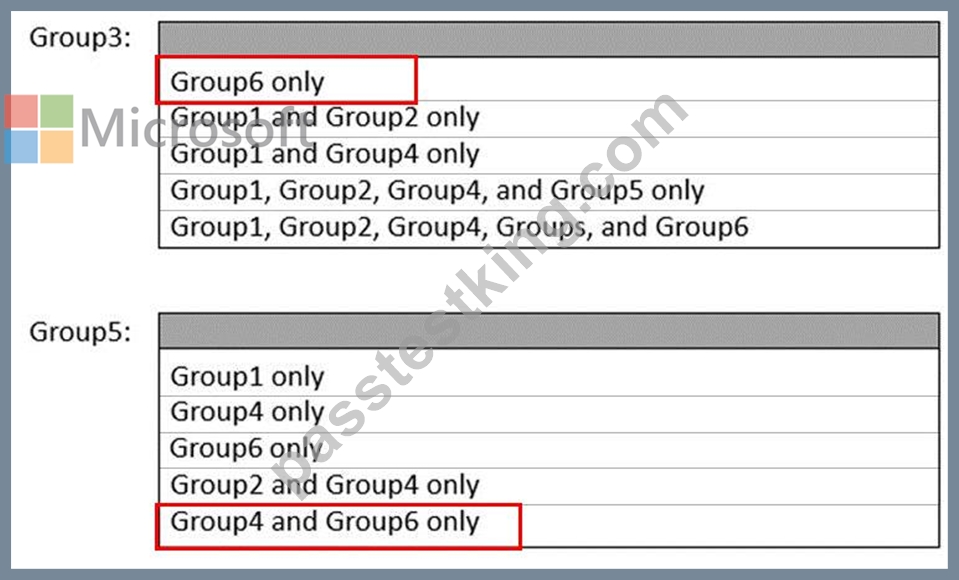
Reference:
https://docs.microsoft.com/en-us/windows/security/identity-protection/access-control/active-directory-security-groups
NEW QUESTION # 166
......
AZ-800 Real Exam Questions and Answers FREE: https://www.passtestking.com/Microsoft/AZ-800-practice-exam-dumps.html
2026 Realistic Verified Free Microsoft AZ-800 Exam Questions: https://drive.google.com/open?id=1oa1uQPM4UjmjioDeMAWJ-HCTc203jbie