
Microsoft Identity and Access Administrator - SC-300 Exam Practice Test
You have a Microsoft Entra tenant that contains the identities shown in the following table.
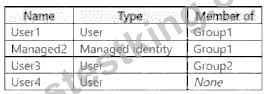
Group1 has the following configurations:
* Owners: User1, User4
* Members: User1, Managed2, Gioup2
You create an access review that has the following settings:
* Name: Review1
* Review scope: Select Teams + Groups
* Group: Group1
* Scope: All users
* Select reviewers: Group owner(s)
The Fallback reviewers: setting is NOT configured.
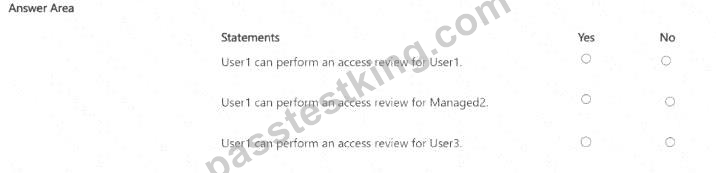
Group1 has the following configurations:
* Owners: User1, User4
* Members: User1, Managed2, Gioup2
You create an access review that has the following settings:
* Name: Review1
* Review scope: Select Teams + Groups
* Group: Group1
* Scope: All users
* Select reviewers: Group owner(s)
The Fallback reviewers: setting is NOT configured.
Correct Answer:
Explanation:
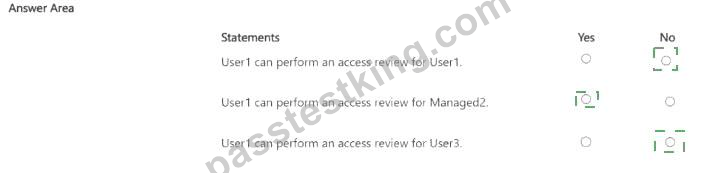
User1 can perform an access review for User1: No
User1 can perform an access review for Managed2: Yes
User1 can perform an access review for User3: Yes
In this scenario, an access review named Review1 has been configured for Group1, with the following conditions:
Review scope: Teams + Groups
Group: Group1
Scope: All users
Reviewers: Group owner(s)
Fallback reviewers: None
From the configuration, the reviewers of the access review are the owners of Group1 - namely User1 and User4. Therefore, both of these users are authorized to review all members of Group1.
Group1 includes the following members:
User1 (User, also owner)
Managed2 (Managed identity)
Group2 (which includes User3)
Since the scope is set to All users, it includes both internal and external members. However, the SC-300 materials emphasize that reviewers cannot review their own access; Microsoft Learn states:
"Reviewers cannot approve or deny their own access in an access review, even if they are members of the group under review." Therefore:
User1 cannot review themselves # No
User1 can review Managed2 # Yes, because Managed2 is a member of Group1 User1 can review User3 # Yes, because User3 is a member of Group2, and Group2 is itself a member of Group1, meaning User3's membership is indirectly part of the review scope This behavior aligns with SC-300 guidance that nested group members are included when the review scope is
"All users," and reviewers (owners) can assess all included members except themselves.
You have a Microsoft 365 subscription.
You plan to deploy an app named App1 that will have the following configurations:
* Will be registered in Microsoft Entra
* Will run as a service without user interaction
* Will collect audit logs associated with user sign-ins
* Will access resources by using the Microsoft Graph API
You need to ensure that App1 can access Microsoft Graph.
What should you use?
You plan to deploy an app named App1 that will have the following configurations:
* Will be registered in Microsoft Entra
* Will run as a service without user interaction
* Will collect audit logs associated with user sign-ins
* Will access resources by using the Microsoft Graph API
You need to ensure that App1 can access Microsoft Graph.
What should you use?
Correct Answer: B
Vote an answer
Explanation: Only visible for PassTestking members. You can sign-up / login (it's free).
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question setsmight have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it as a result, these questions will not appear in the review screen.
You have an Amazon Web Services (AWS) account, a Google Workspace subscription, and a GitHub account.
You deploy an Azure subscription and enable Microsoft 365 Defender.
You need to ensure that you can monitor OAuth authentication requests by using Microsoft Defender for Cloud Apps.
Solution: From the Microsoft 365 Defender portal, you add the Google Workspace app connector.
Does this meet the goal?
After you answer a question in this section, you will NOT be able to return to it as a result, these questions will not appear in the review screen.
You have an Amazon Web Services (AWS) account, a Google Workspace subscription, and a GitHub account.
You deploy an Azure subscription and enable Microsoft 365 Defender.
You need to ensure that you can monitor OAuth authentication requests by using Microsoft Defender for Cloud Apps.
Solution: From the Microsoft 365 Defender portal, you add the Google Workspace app connector.
Does this meet the goal?
Correct Answer: B
Vote an answer
Explanation: Only visible for PassTestking members. You can sign-up / login (it's free).
You have two Microsoft Entra tenants named contoso.com and fabrikam.com. Contoso.com contains the identities shown in the following table.
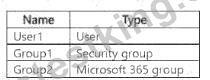
You configure cross-tenant synchronization from contoso.com to fabrikam.com. Which identities will sync with fabrikam.com?
You configure cross-tenant synchronization from contoso.com to fabrikam.com. Which identities will sync with fabrikam.com?
Correct Answer: C
Vote an answer
You have an Azure subscription named Sub1 that contains a virtual machine named VM1.
You need to enable Microsoft Entra login for VM1 and configure VM1 to access the resources in Sub1.
Which type of identity should you assign to VM1?
You need to enable Microsoft Entra login for VM1 and configure VM1 to access the resources in Sub1.
Which type of identity should you assign to VM1?
Correct Answer: B
Vote an answer
Explanation: Only visible for PassTestking members. You can sign-up / login (it's free).
You have an on-premises datacenter that contains the hosts shown in the following table.
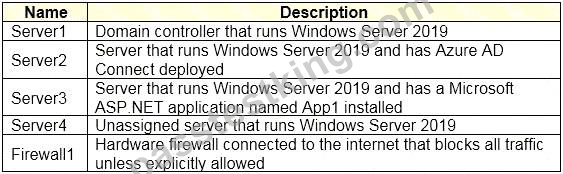
You have an Azure Active Directory (Azure AD) tenant that syncs to the Active Directory forest. Multi-factor authentication (MFA) is enforced for Azure AD.
You need to ensure that you can publish App1 to Azure AD users.
What should you configure on Server and Firewall1? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.
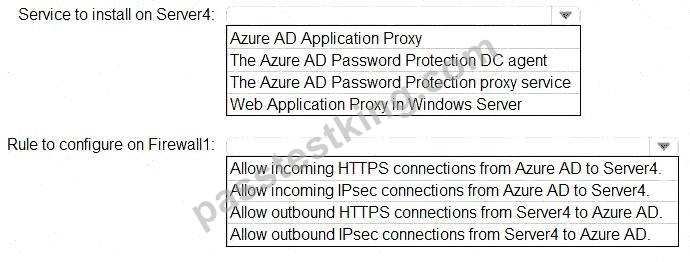
You have an Azure Active Directory (Azure AD) tenant that syncs to the Active Directory forest. Multi-factor authentication (MFA) is enforced for Azure AD.
You need to ensure that you can publish App1 to Azure AD users.
What should you configure on Server and Firewall1? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.
Correct Answer:
Explanation:
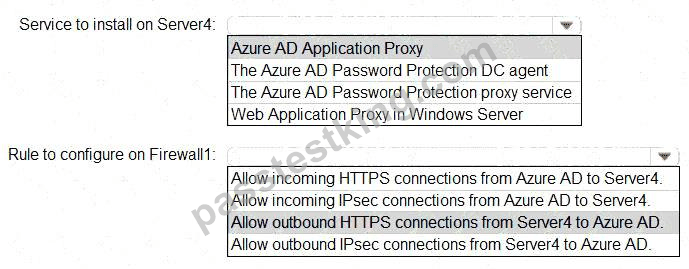
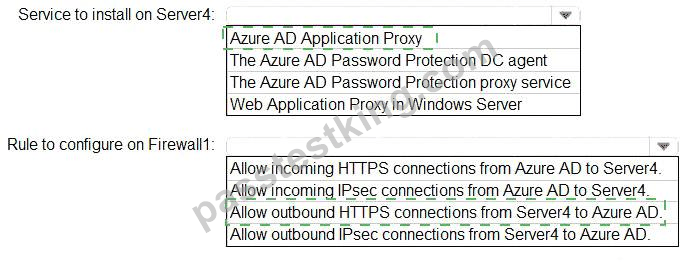
In SC-300, publishing an on-premises web app to Azure AD users is performed with Azure AD Application Proxy. The exam materials and Microsoft curriculum explain that you deploy an Application Proxy connector on a Windows Server joined to your on-premises network, which brokers requests to internal apps such as an ASP.NET site. The connector is designed for perimeter-friendly deployments: "Application Proxy connectors only make outbound connections to the Application Proxy service" and "no inbound ports need to be opened in the firewall." Because the connector initiates the session to Azure over TLS, the firewall requirement is simply to permit the connector's outbound HTTPS to the service endpoints. This aligns with the least- exposure pattern emphasized in Identity Governance: you avoid publishing inbound listener rules and still support Azure AD features like Conditional Access and MFA at the cloud edge. Alternatives in the list do not meet the publishing requirement: the Password Protection DC agent and Password Protection proxy service are for banned-password enforcement, and Web Application Proxy in Windows Server is a different reverse- proxy technology not required when using Azure AD Application Proxy. Therefore, to publish App1 securely to Azure AD users, install Azure AD Application Proxy on Server4 and allow outbound HTTPS from Server4 through Firewall1.
You have an on-premises app named Appl. You have a Microsoft Entra tenant You plan to publish App1 by using Microsoft Entra Private Access. You need to enable the Private access profile. Which blade should you use in the Microsoft Entra admin center?
Correct Answer: B
Vote an answer
You have an Azure subscription named Sub1.
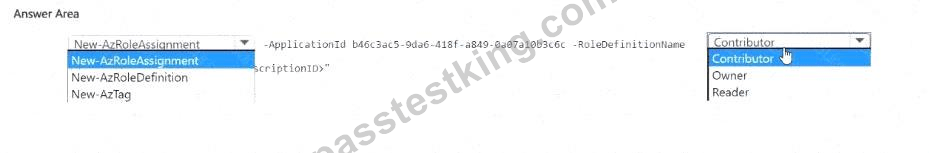
You plan to deploy Microsoft Entra Permissions Management.
You need to ensure that Permission Management can onboard Sub1. The solution must follow the principle of least privilege.
How should you complete the PowerShell command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You plan to deploy Microsoft Entra Permissions Management.
You need to ensure that Permission Management can onboard Sub1. The solution must follow the principle of least privilege.
How should you complete the PowerShell command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:
Explanation:
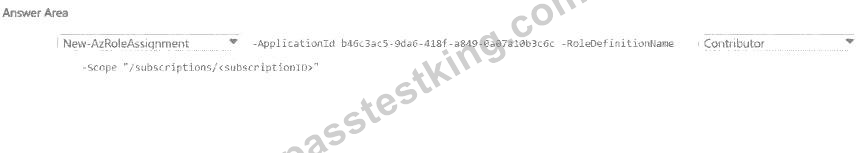
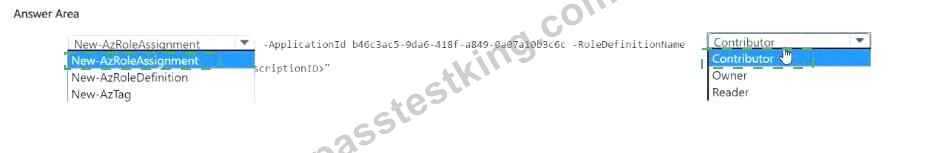
In Microsoft Entra Permissions Management (formerly CloudKnox), onboarding an Azure subscription requires granting the Permissions Management service principal the minimum rights needed to discover identities, roles, and permissions across that subscription. The SC-300 materials emphasize the principle of least privilege for onboarding: assign Reader at the subscription scope so the service can inventory resources and permissions without the ability to change them. After onboarding, if you want automated remediation
/right-sizing, you can additionally grant User Access Administrator (or perform changes manually), but that elevation is not required merely to onboard and collect data.
Accordingly, you complete the PowerShell by creating an RBAC assignment for the application (service principal) at the subscription scope using New-AzRoleAssignment and specifying -RoleDefinitionName Reader. Creating a new custom role (New-AzRoleDefinition) is unnecessary, and New-AzTag is unrelated to RBAC. Choosing Owner or Contributor would exceed the access required for onboarding and violate least- privilege guidance. The correct, minimal configuration is therefore: assign Reader to the Permissions Management application at the /subscriptions/ < SubscriptionId > scope using New-AzRoleAssignment.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it as a result, these questions will not appear in the review screen.
You have an Amazon Web Services (AWS) account, a Google Workspace subscription, and a GitHub account.
You deploy an Azure subscription and enable Microsoft 365 Defender
You need to ensure that you can monitor OAuth authentication requests by using Microsoft Defender for Cloud Apps.
Solution: From the Microsoft 365 Defender portal, you add the Microsoft Azure app connector.
Does this meet the goal?
After you answer a question in this section, you will NOT be able to return to it as a result, these questions will not appear in the review screen.
You have an Amazon Web Services (AWS) account, a Google Workspace subscription, and a GitHub account.
You deploy an Azure subscription and enable Microsoft 365 Defender
You need to ensure that you can monitor OAuth authentication requests by using Microsoft Defender for Cloud Apps.
Solution: From the Microsoft 365 Defender portal, you add the Microsoft Azure app connector.
Does this meet the goal?
Correct Answer: A
Vote an answer
Explanation: Only visible for PassTestking members. You can sign-up / login (it's free).
You need to implement the planned changes for litware.com. What should you configure?
Correct Answer: B
Vote an answer
Explanation: Only visible for PassTestking members. You can sign-up / login (it's free).